Know Your VulnerabilitiesBefore Adversaries Do
AI-powered application security platform. Hunt backdoors and supply-chain implants, run deep code audits, generate custom Semgrep rules and executive reports — with an MCP server that lets your AI assistant manage it all.
Trace risk to a safe fix
Watch Guardian triage a fictional repository, then inspect or replay any step yourself.
Inside the product
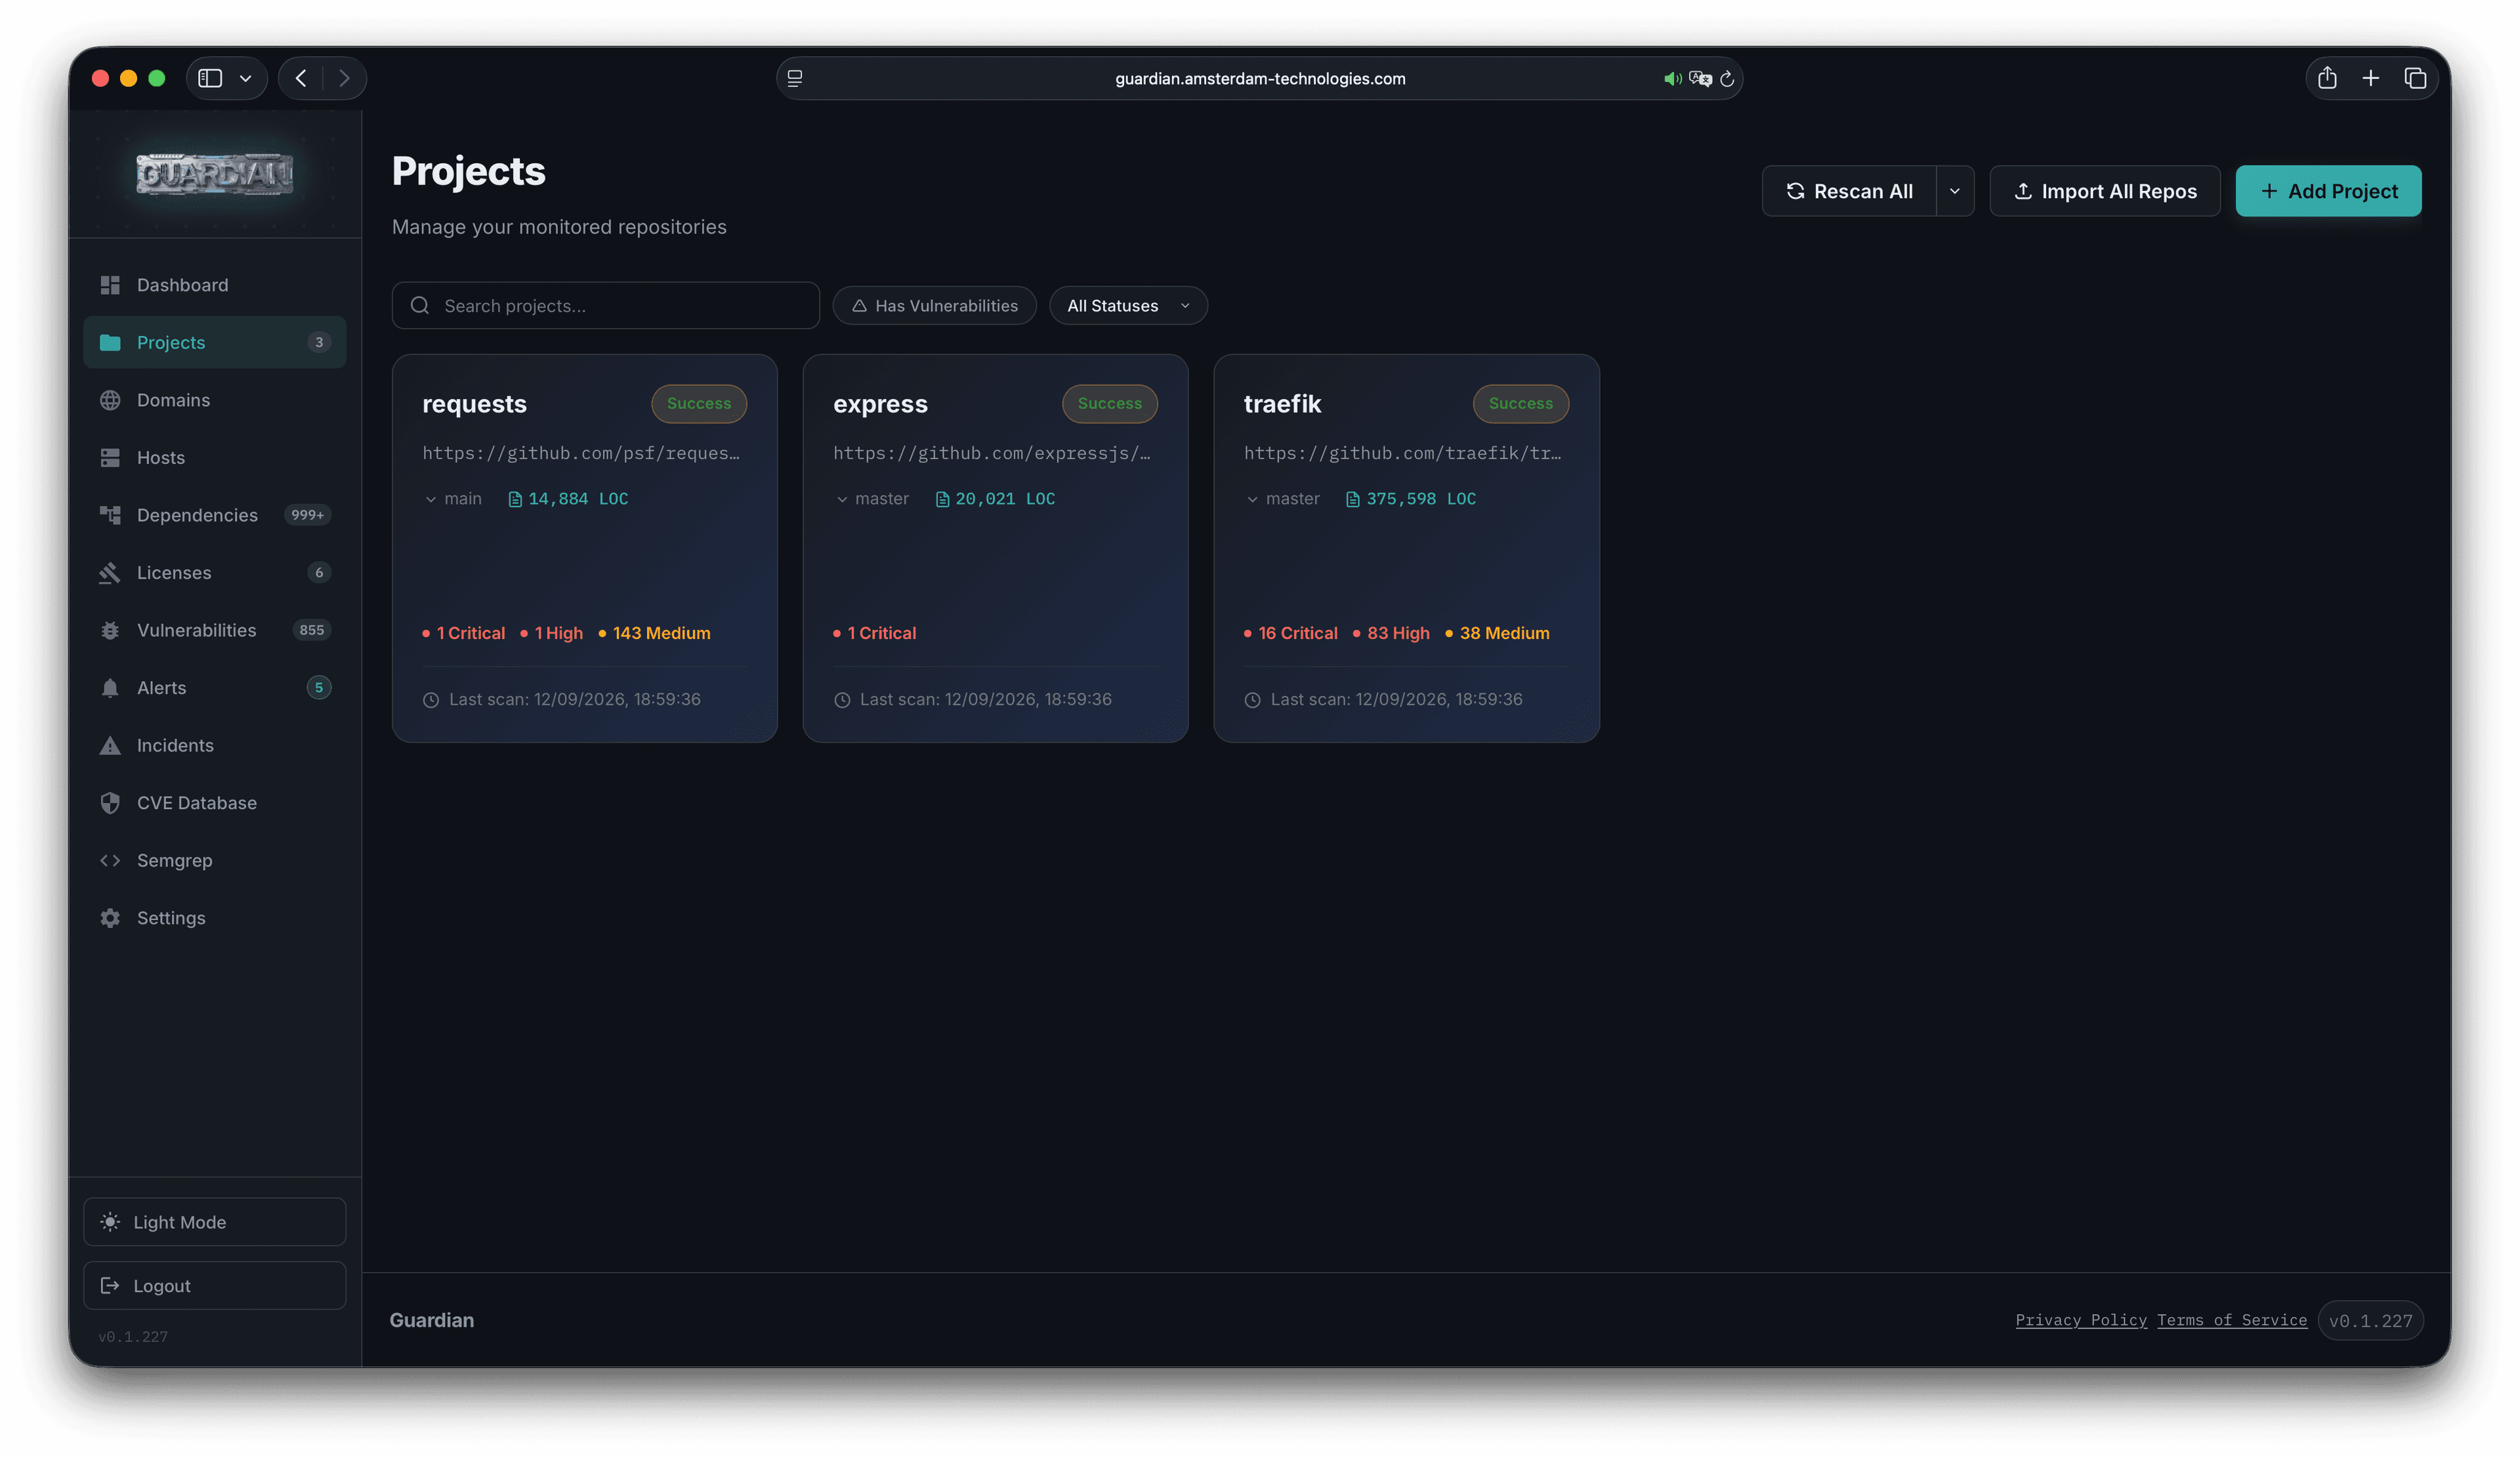
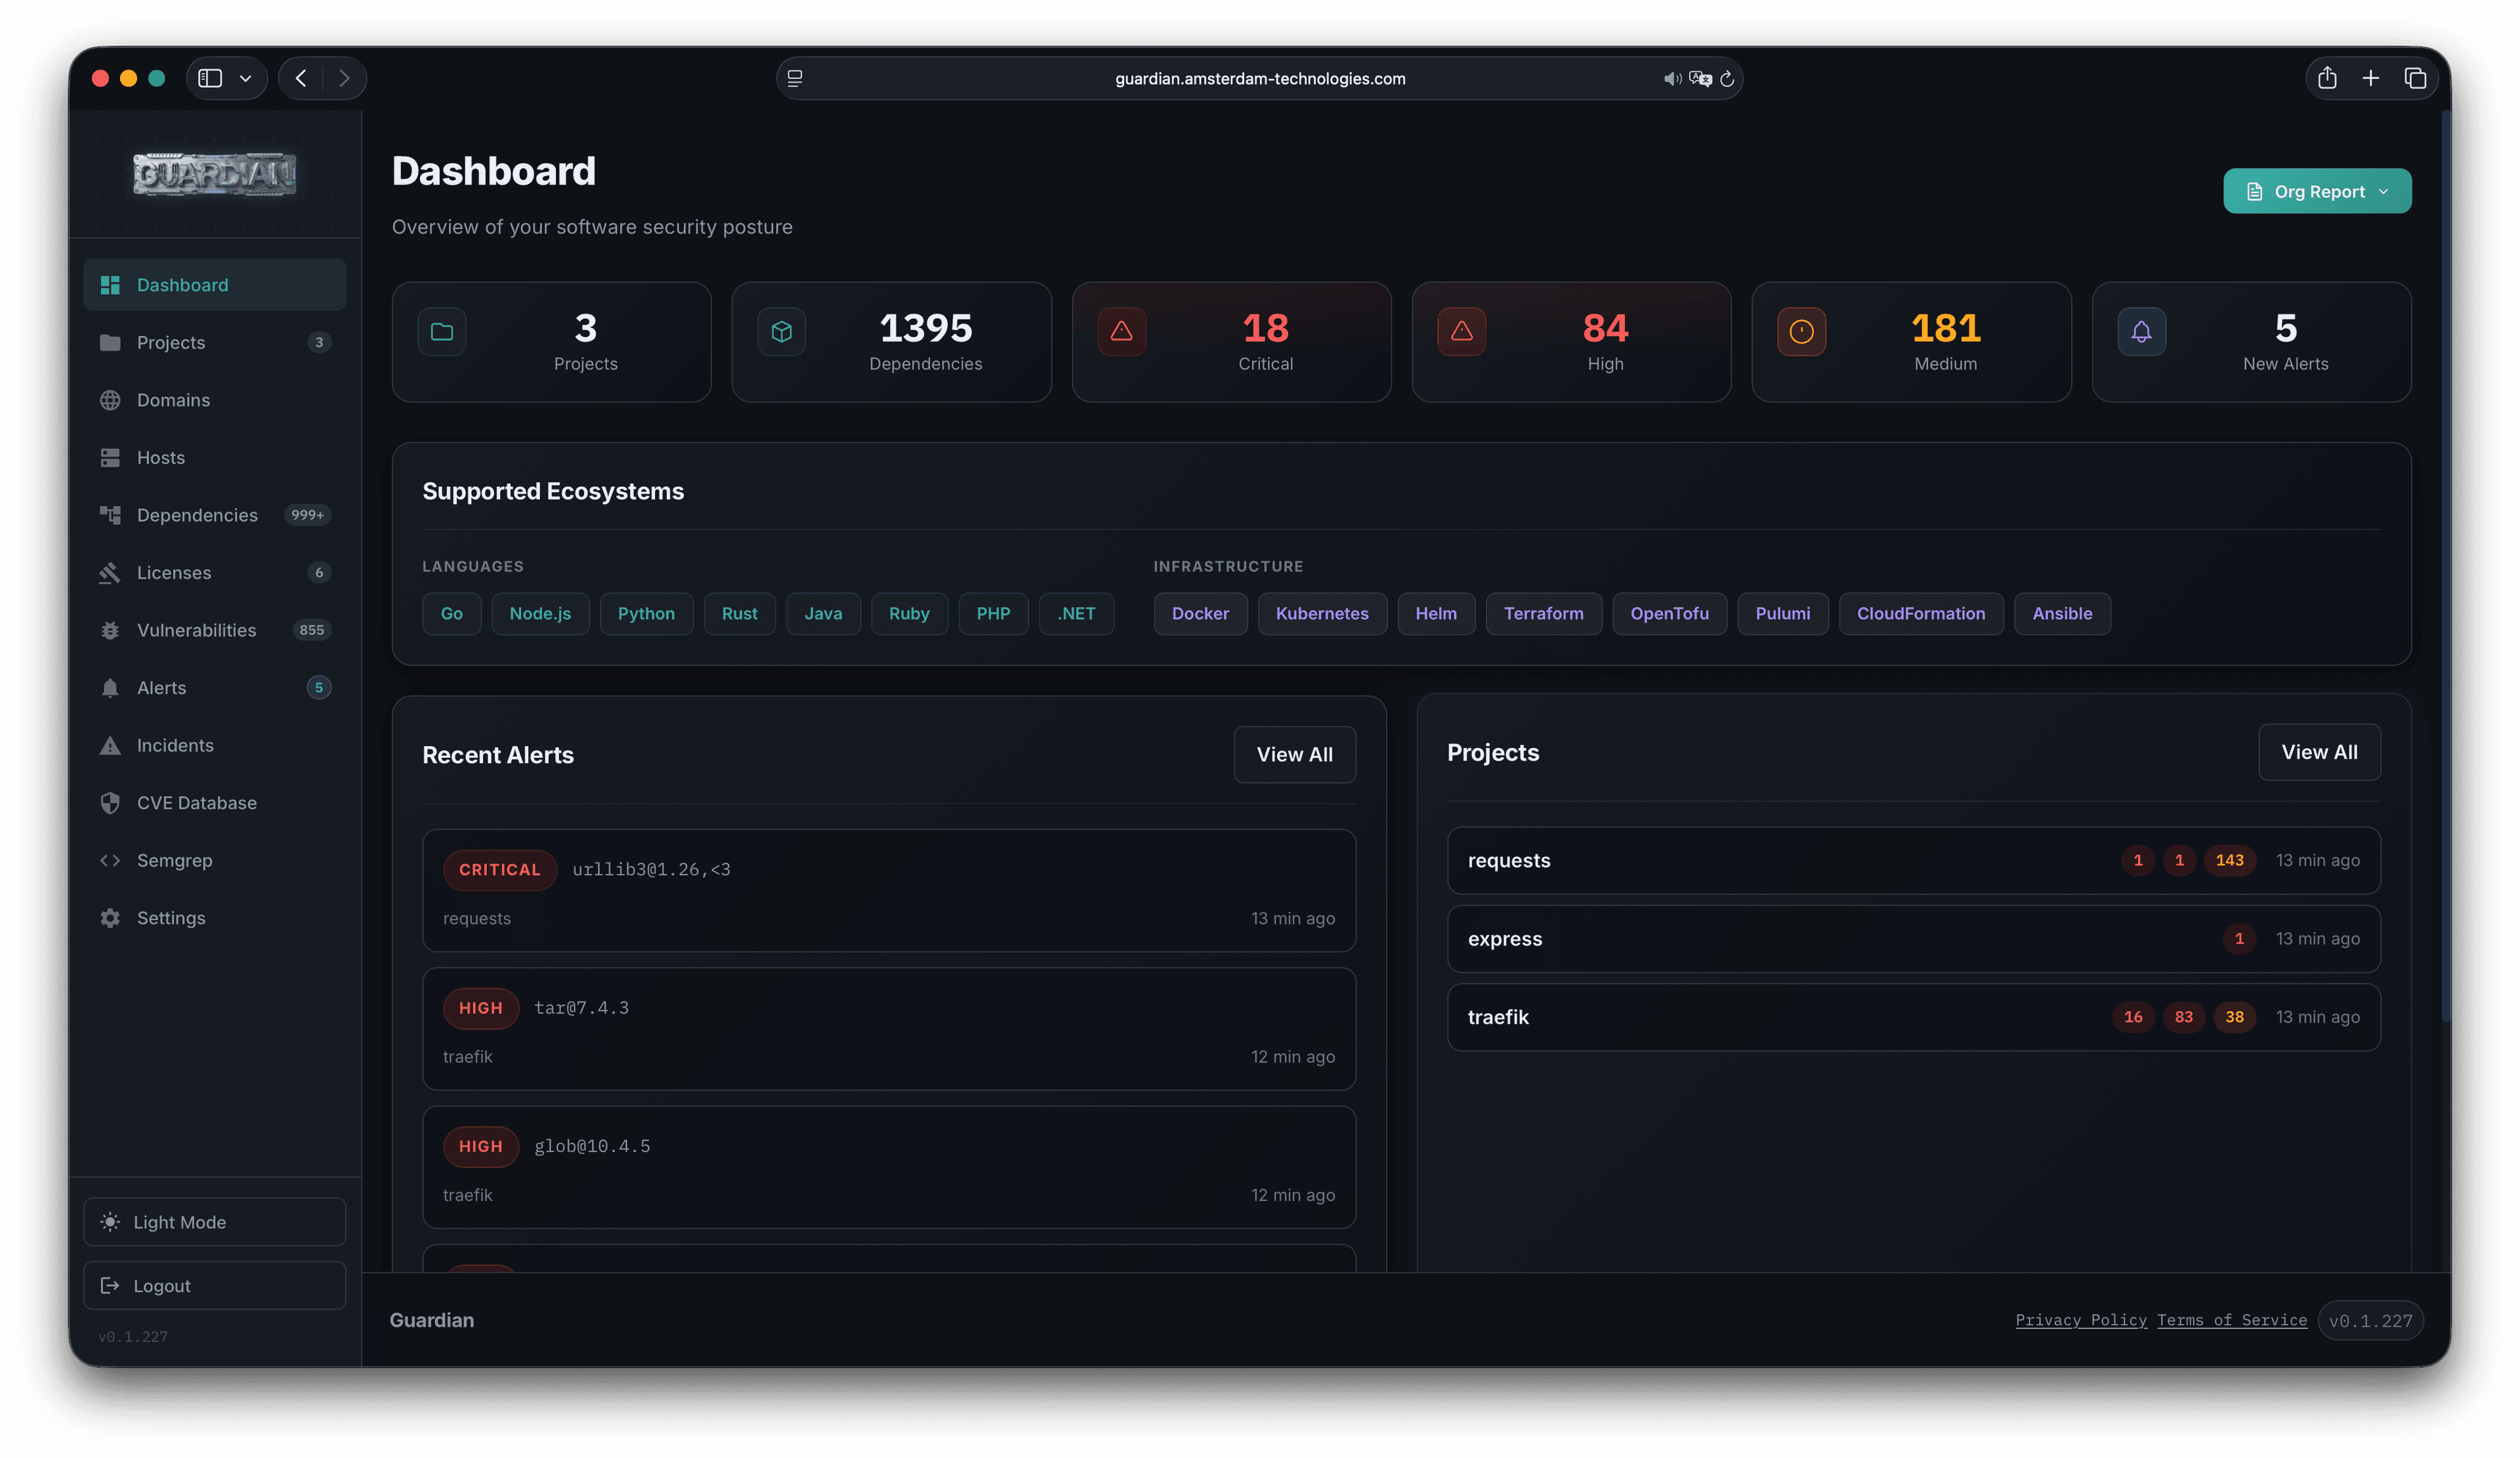
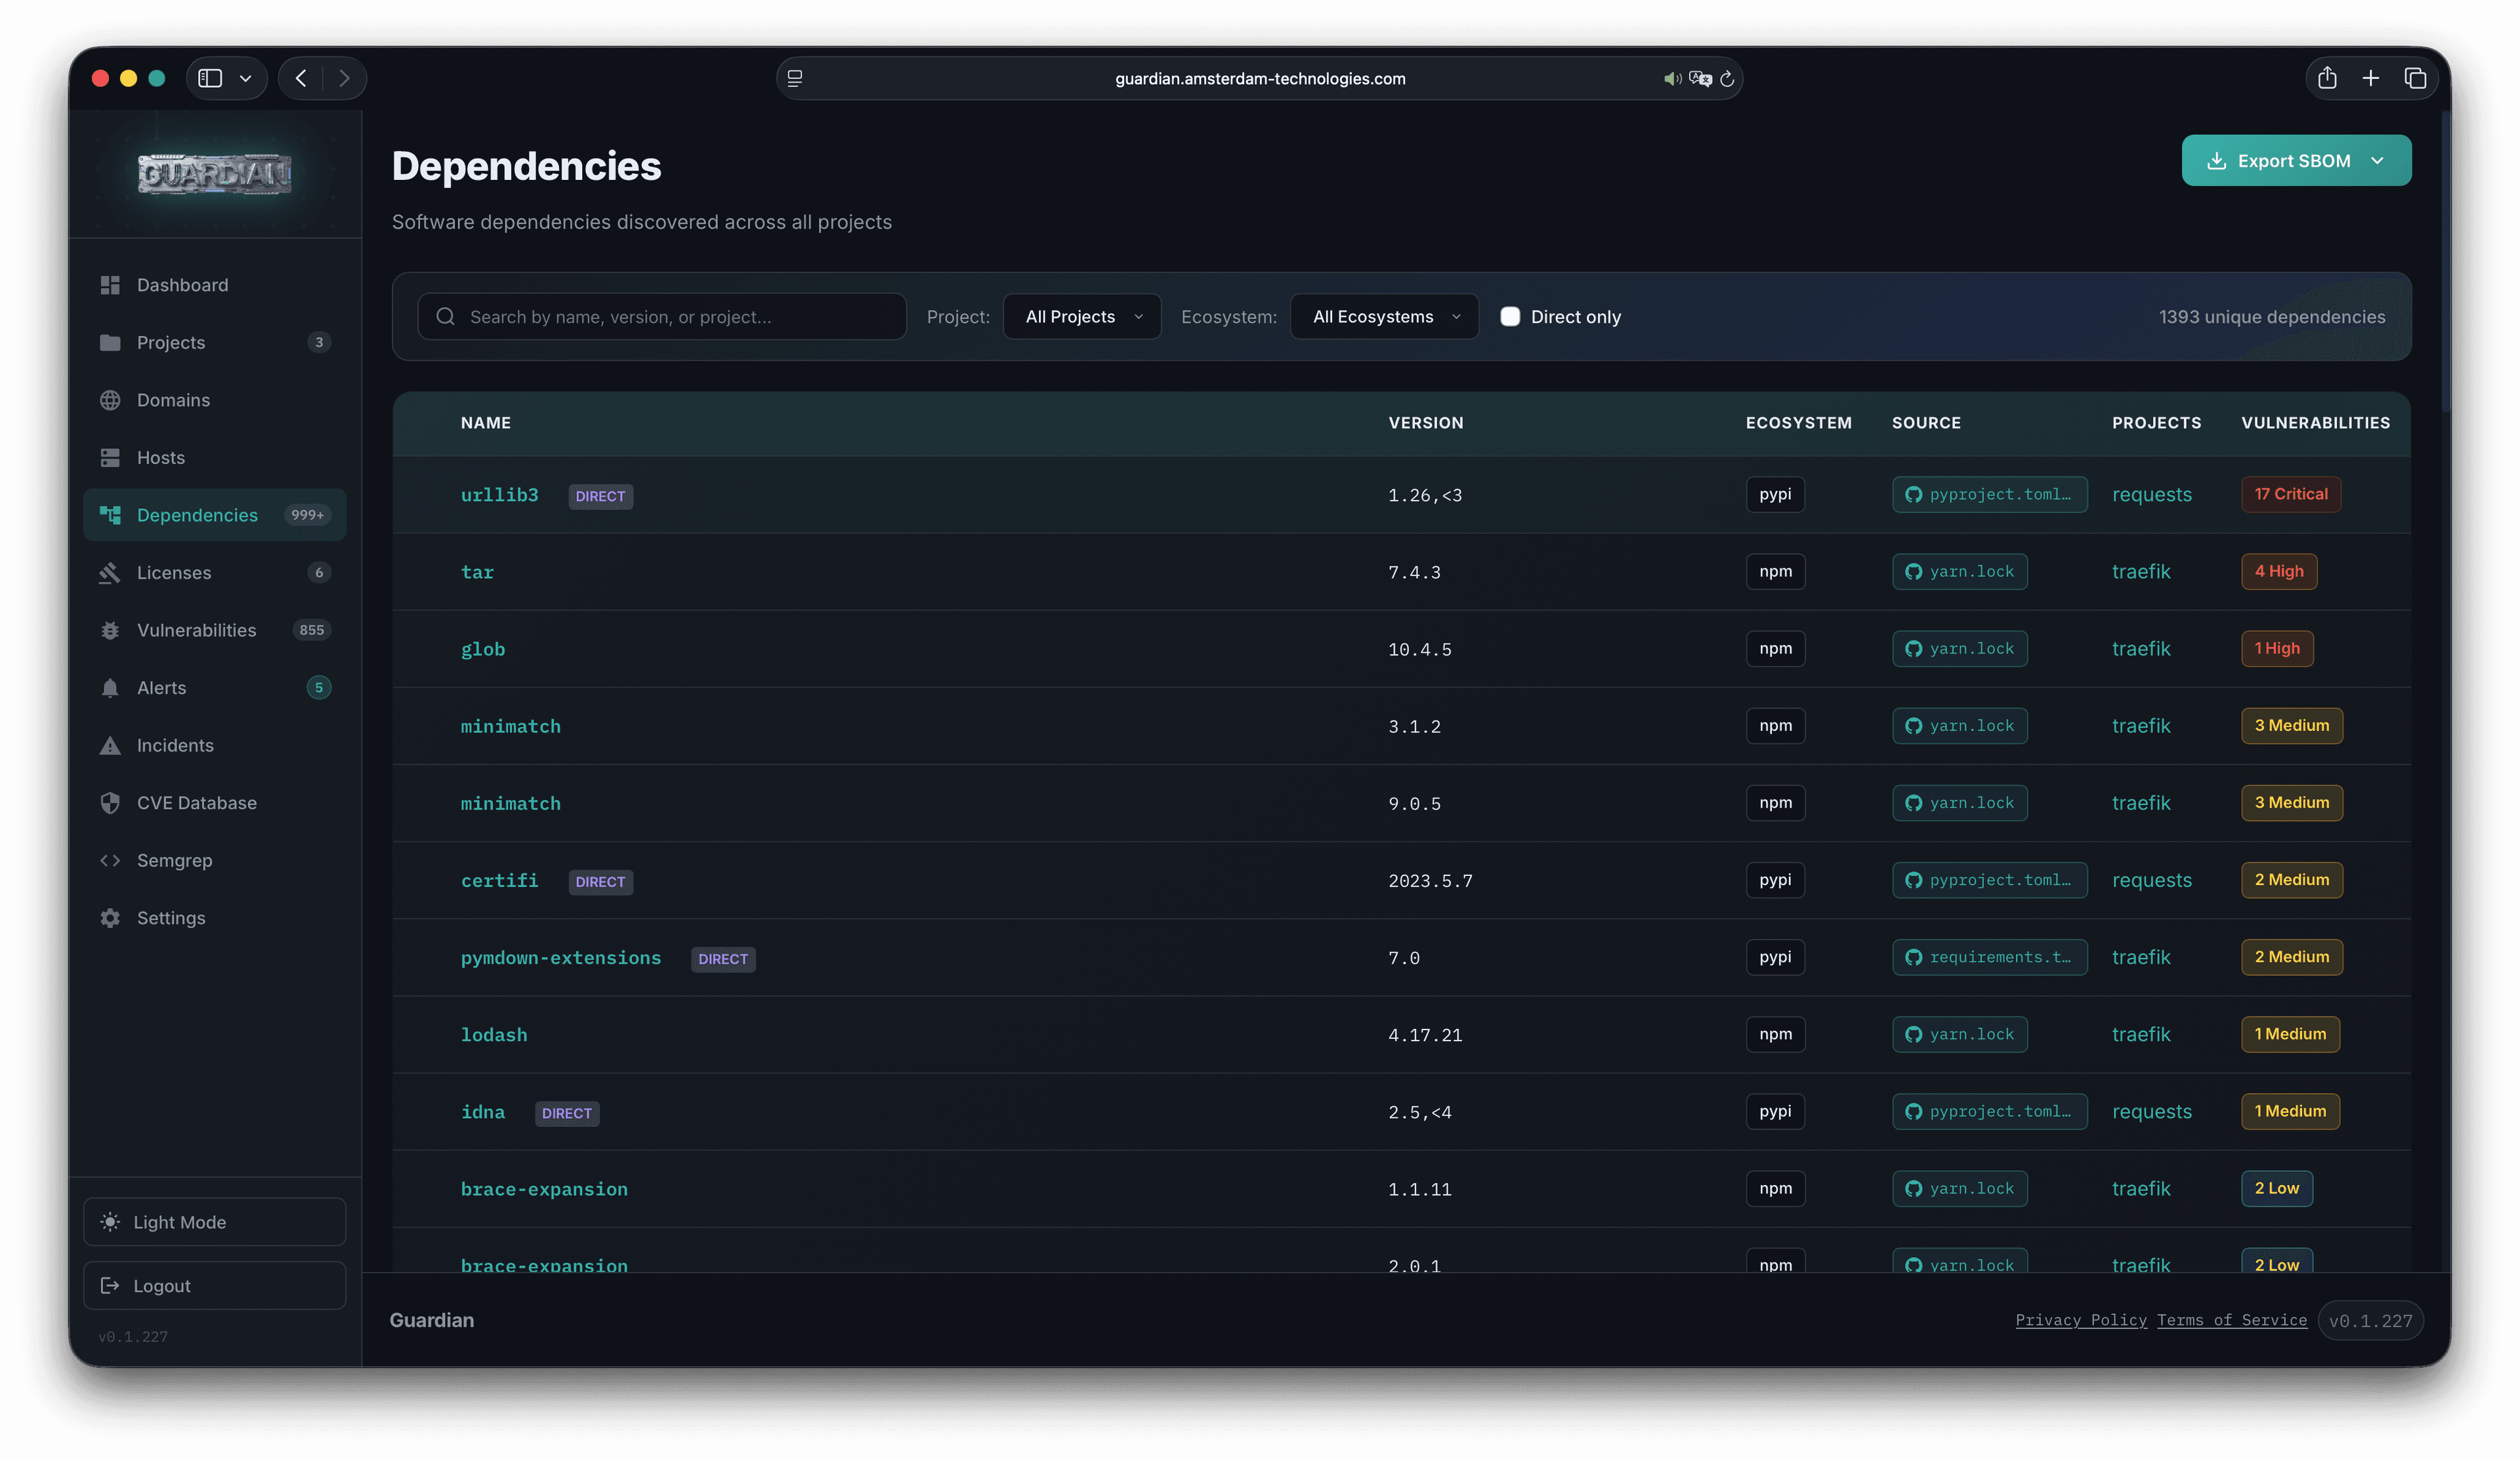
Turn Application Risk into Action
Connect dependencies, vulnerabilities, licenses, alerts, and code scans in one application security workflow.
Security Chaos Across Your Stack
Dependabot noise, CVE feeds and scanner output pile up faster than any team can triage by hand
Scattered Alerts
Dependabot alerts drowning each repo. No central view of what actually matters.
Manual Tracking
Maintaining spreadsheets of versions is tedious and always outdated.
Slow Response
When a critical CVE drops, you need answers in minutes, not hours.
Five Agents, Each With One Job
Hunt implants, audit code, assess exploitability, generate Semgrep rules, and draft the report — five AI agents that each own a single task
AI Security Audit
Deep 3-phase code analysis finds logic flaws, race conditions, and design issues that traditional SAST tools miss entirely.
Malicious Code Investigator
Adversarial AI red-team agent hunts for backdoors, implants, and supply-chain compromises — referencing real-world incidents like tj-actions, ua-parser-js, and XZ utils.
Vulnerability Assessment
AI reviews every finding for real-world exploitability. Assigns relevance scores, detects false positives, and generates proof-of-concept exploits.
Custom Semgrep Rules
A 4-agent pipeline analyzes your codebase and generates targeted security rules. Per-project customization catches what generic rulesets miss.
Executive Reports
Generate org-wide and per-project security reports with AI-written executive summaries, risk assessments, and prioritized remediation guidance.
Your AI Assistant Speaks Guardian
A full Model Context Protocol server lets Claude Code, Cursor, Windsurf, and other AI tools directly query and manage your security posture
What Guardian Watches
Dependency intelligence, SAST, SBOMs, malicious-code detection and licence tracking, from one connected repository list
Multi-VCS Integration
Connect GitHub, GitLab, Bitbucket, Azure DevOps, Gitea, or SVN repositories. We automatically discover all dependency files and track versions in real-time.
Dependency Discovery
18+ ecosystems supported: Go, Node.js, Python, Rust, Java, Ruby, PHP, .NET, Docker, Kubernetes, Helm, Terraform, and more.
Multi-Source Vulnerability Intelligence
Aggregated data from three open-source vulnerability databases: GitHub Advisory Database (GHSA) and Google OSV for package vulnerabilities, plus NVD for enriched CVE details with CVSS scoring and CPE matching.
Instant Alerts
Get notified immediately when a new vulnerability affects any of your tracked versions. Email, Slack, or webhooks.
SBOM Generation
Export CycloneDX and SPDX 2.3 compliant SBOMs for compliance. One click per project, always up-to-date.
SAST Scanning
Static Application Security Testing with 15+ tools. Find vulnerabilities in source code with CWE-based deduplication.
Malicious Code & Supply-Chain Detection
Hunts for backdoors, implants, and supply-chain compromises beyond CVE matching. Four deterministic detectors (typosquatting, install-hook abuse, committed binaries with optional YARA, malicious Dockerfile/CI patterns, source backdoors) plus a dedicated AI red-team agent that investigates with adversarial intent.
GitHub App Integration
Install the Guardian GitHub App for fine-grained, tokenless repository access. Automatic webhook-driven scans on every push and pull request. OAuth installation flow with zero PAT management.
AI Security Audit
A 3-phase AI agent explores your codebase to find logic flaws, race conditions, TOCTOU bugs, and insecure design patterns that static analysis cannot detect.
AI Vulnerability Assessment
Every finding is reviewed for real-world exploitability with a 0.0-1.0 relevance score. False positives are identified automatically. Proof-of-concept generation validates true threats.
Custom Semgrep Rules
A 4-agent AI pipeline generates project-specific security rules targeting your exact tech stack. Org-level and per-project rule hierarchies with granular control.
Executive Security Reports
AI-generated org-wide and per-project reports with executive summaries, risk assessments, top risks, and prioritized recommendations. Export as PDF or Markdown.
MCP Server
33 tools across query, analysis, and action categories. Let Claude Code, Cursor, or any MCP-compatible AI assistant directly manage your security posture.
Asset Monitoring
Monitor your attack surface with passive DNS-based subdomain discovery. Automatically discover live domains and subdomains, track IP addresses, and get visibility into your external-facing assets across all projects.
License Tracking
Automatically detect licenses in all your dependencies. Get alerts when forbidden licenses like GPL or AGPL are found. Ensure compliance across all projects.
Central Dashboard
One dashboard lists every project, finding and dependency, filterable by severity or ecosystem. Filter by severity, ecosystem, or project.
Download the Guardian Whitepaper
Application security platform covering malicious-code & backdoor detection, supply-chain analysis, SAST, AI-powered auditing, and MCP integration.
Connect Any Repository
GitHub, GitLab, Bitbucket, Azure DevOps, Gitea and plain Git remotes — hosted or self-hosted
GitHub
First-class GitHub App with OAuth installation flow, automatic webhook-driven scans on push and PR events. Also supports PAT and GitHub Enterprise Server.
GitLab
GitLab.com and self-hosted GitLab instances with custom URL configuration
Bitbucket
Bitbucket Cloud integration with workspace and repository access
Azure DevOps
Azure Repos integration with organization and project support
Gitea
Gitea and Forgejo self-hosted instances with configurable base URL
SVN
Apache Subversion support with full checkout capabilities for legacy systems
Supported Ecosystems
18+ ecosystems, from go.mod and Cargo.toml to Terraform lock files
Languages & Package Managers
Containers & Infrastructure
Development Tools
Ask Your Own Codebase
Ask about a CVE, a licence or a dependency and get the answer from your own project index
Stay up to date with Guardian
Release notes, technical deep-dives and product updates. No spam, and you can unsubscribe at any time.
Start Monitoring Your Assets
Connect a repository and the first findings arrive within minutes. No credit card required.